Free trail to download before payment
Our SC-200日本語 exam study material, known as one of the reliable SC-200日本語 exam training material provider, has a history of over ten years. We are committed to making customers have a good experience in using our SC-200日本語 training material. Moreover, we sincere suggest you to download a part of free trail to see if you are content with our Microsoft SC-200日本語 exam study material and know how to use it properly. Our web page provides free demo for you to have a good choice.
24/7 customer support secure shopping site
Our SC-200日本語 exam study material recognizes the link between a skilled, trained and motivated workforce and the company's overall performance. We offer instant support to deal with your difficulties about our SC-200日本語 exam prep training. As long as you leave us a message and send us an email, we will do our best to resolve your problem. Any time is available, for we are waiting for your belief in our SC-200日本語 exam training material. So do not hesitate to let us know your trouble, we promise to give you a satisfied reply.
Microsoft SC-200日本語 braindumps Instant Download: Our system will send you the SC-200日本語 braindumps file you purchase in mailbox in a minute after payment. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Certification Topics of Microsoft SC-200 Exam
Mitigate threats using Microsoft 365 Defender (25-30%)
Mitigate threats using Azure Defender (25-30%)
Mitigate threats using Azure Sentinel (40-45%)
Reference: https://docs.microsoft.com/en-us/learn/certifications/exams/sc-200
Why Microsoft SC-200 certification is worth it
If you are a computer expert, you need to be recommended by another person who is also certified in order to get the certification. If you have several certifications and can prove they are valid, you may qualify for an online exam that leads to an SC-200 certification. Microsoft's Security Operations Analyst Certification is only available in the USA, Canada, UK, and Singapore. This certificate proves your knowledge about security threat management, vulnerability management, and security audit management. You are given this certificate if you pass the exam with a score of at least 70%. The Security Operations Associate (SC-200) is a Microsoft Certified Technology Specialist certification that focuses on information security operations. It is not just about computer networks; it also covers disaster recovery, risk assessment, and business continuity planning. The sc-200 test is based on the job role of people involved in information security operations. They are responsible for applying security policies in the workplace and maintaining these policies through assessing vulnerabilities and managing risks.
Our company is thoroughly grounded in our values. We demand of ourselves and others the highest ethical standards and our processes of SC-200日本語 exam study material will be of the highest quality. Our Microsoft SC-200日本語 valid study guide is deeply committed to meeting the needs of our customers, and we constantly focus on customer satisfaction. That is the also the reason why we play an active role in making our Microsoft Certified: Security Operations Analyst Associate SC-200日本語 exam training material into which we operate better exam materials to help you live and work.
Nowadays, our understanding of the importance of information technology has reached a new level. Information technology is developing rapidly. Economies are becoming globalized. Our SC-200日本語 exam prep training is considered as one of the most useful and cost-efficient applications for those who are desired to get the SC-200日本語 exam certification. You may have doubts why our SC-200日本語 latest pdf vce are so attracted; you can get answers after reading the following items.
Now, please pay attention to our SC-200日本語 latest vce prep.

What is the easiest way to pass my Microsoft SC-200 Exam
Passing your Microsoft SC-200 Exam is a breeze after you have studied with the Microsoft SC-200 practice test. I had previously bought study guides for this exam and did not feel confident about taking my exam. I had already passed the exam once before, but it was over ten years ago so I was nervous about doing it again. Microsoft SC-200 study guide provided me with everything that I needed to pass with flying colors! In fact, I felt so confident after studying with their comprehensive guide that I just knew that I would pass. After all, they did not lead me astray on my first attempt and they were not going to do it again. The Microsoft SC-200 Exam is not easy, but the Microsoft SC-200 exam dumps make it easy to succeed! The moment that I logged into their website, I found all of the information that I needed right there. It was so much easier than trying to find answers to questions in the book or online somewhere else. It was all right there for me to work with and because of this, it really sped up the process of learning for me. I highly recommend using practice test products if you are interested in passing on your first try. They have never steered me wrong!
Professional upgrade check everyday
We constantly accelerate the development of our R & D as well as our production capabilities with super capacity, advanced technology, flexibility as well as efficiency. Therefore, our professional experts attach importance to checking our SC-200日本語 exam study material so that we can send you the latest SC-200日本語 updated study pdf. Do not be worried about your accommodation to the new SC-200日本語 exam; we just update to simulate real exam scenarios so you can learn more professional knowledge.
Highly efficient learning plan
Long-term training doesn't seem to be suitable for anyone. And it's easier to feel tired when you study before the Microsoft Certified: Security Operations Analyst Associate SC-200日本語 exam study material for a long time. But you don't need to spend so much time in practicing with our SC-200日本語 exam study material. We provide a scientific way for you to save your time and enhance the efficiency of learning. 20-30 hours' practice is designed for most of the workers, which means they can give consideration to their preparation for the SC-200日本語 exam and their own business.
Microsoft SC-200日本語 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Perform threat hunting | 20–25% | - Plan and prepare threat hunts
|
| Topic 2: Manage security operations environment | 40–45% | - Configure Microsoft Defender XDR
|
| Topic 3: Respond to security incidents | 35–40% | - Contain, eradicate, and recover
|
Microsoft Security Operations Analyst (SC-200日本語版) Sample Questions:
お客様は、Microsoft Defenderを使用するMicrosoft 365 E5サブスクリプションと、Azure Sentinelを使用するAzureサブスクリプションをお持ちです。
既知の悪意のあるメール送信者から送信されたメールに含まれるファイルを持つすべてのデバイスを特定する必要があります。クエリはSHA256ハッシュの一致に基づいて実行されます。
質問にはどのように回答すればよいですか?回答するには、回答欄で適切なオプションを選択してください。
注:正解ごとに1ポイントが加算されます。
Correct Answer:

Explanation: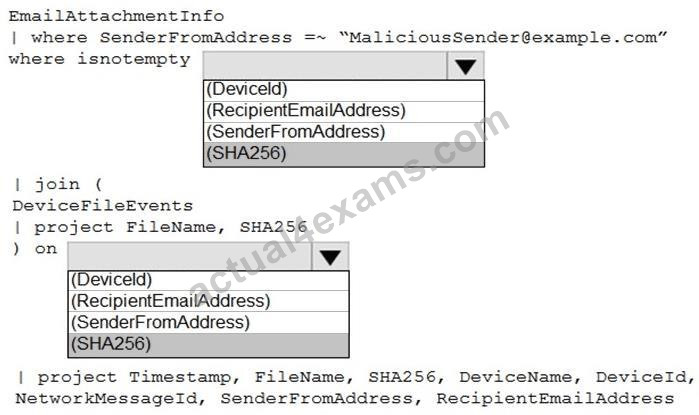
To correlate malicious email attachments with endpoints, Microsoft Defender data schemas expose attachment metadata in EmailAttachmentInfo (including the SHA256 hash) and endpoint file activity in DeviceFileEvents (which also records SHA256 for observed files). The recommended investigation pattern is:
(1) filter email telemetry to the suspected sender and keep only attachments with a populated hash; (2) join that result with endpoint file events on the SHA256 hash to find devices where an identical file (by cryptographic hash) was seen. In KQL, isnotempty(SHA256) ensures you only pass attachments with a valid hash to the join, and join ... on SHA256 performs an exact-match correlation across datasets. This method aligns with Defender's guidance to use hash-based correlation as the most reliable way to match artifacts across different security workloads (email vs. endpoint), since filenames and paths can change, but a cryptographic hash uniquely identifies file content. The final project selects operational fields for response- timestamps, file name and hash, device identifiers/names, message IDs, and sender/recipient-so the SOC can quickly pivot to the impacted devices and the original email that delivered the file.
お客様は、Microsoft Defender XDRを使用するMicrosoft 365 E5サブスクリプションをご利用されています。
Microsoft Sentinelワークスペースをお持ちです。
Microsoft Sentinelコネクタは、次の表に示すように構成されます。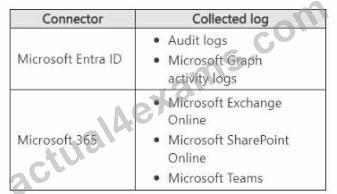
Microsoft Sentinel を使用して、条件付きアクセス ポリシーに関連する疑わしい Microsoft Graph API アクティビティを調査します。以下のアクティビティを検索する必要があります。
* PowerShellを使用して条件付きアクセス ポリシーをダウンロードする
* Microsoft Entra 管理センターを使用して条件付きアクセス ポリシーを更新します。各アクティビティに対してどのテーブルをクエリする必要がありますか? 回答するには、回答領域で適切なオプションを選択します。
注:正解ごとに1ポイントが加算されます。
Correct Answer:

Explanation:
For Conditional Access investigations in Microsoft Sentinel, the data source depends on the control plane used. When policies are downloaded via PowerShell, the cmdlets call the Microsoft Graph (e.g., Get- MgIdentityConditionalAccessPolicy). Those Graph requests are captured by the Microsoft Graph Activity Logs connector and land in the MicrosoftGraphActivityLogs table. This table records the app identity (such as PowerShell/Graph SDK), the API path (like /identity/conditionalAccess/policies), verb (GET), and result, which is ideal for spotting bulk reads/exports of policy definitions.
When policies are updated in the Microsoft Entra admin center, two streams provide visibility. First, directory auditing writes change events (create/update/delete of Conditional Access policies) to Microsoft Entra Audit logs, surfaced in Sentinel as the AuditLogs table, including the actor, target policy, operation (Update policy), and result. Second, the Entra admin center itself is a first-party application that performs the update by invoking Microsoft Graph; those API calls are also recorded in MicrosoftGraphActivityLogs (with verb PATCH/POST and the policy resource path).
Therefore, to cover both perspectives-the authoritative audit record and the underlying API activity-you should query AuditLogs and MicrosoftGraphActivityLogs for updates, and MicrosoftGraphActivityLogs for downloads executed through PowerShell.
sws1 という名前の Microsoft Sentinel ワークスペースがあります。
ユーザーが異常に多数のAzure ADユーザーアカウントを作成したことを検出するクエリを作成する必要があります。
質問にはどのように回答すればよいですか?回答するには、回答欄で適切なオプションを選択してください。
注:正解ごとに1ポイントが加算されます。
Correct Answer:
Explanation:
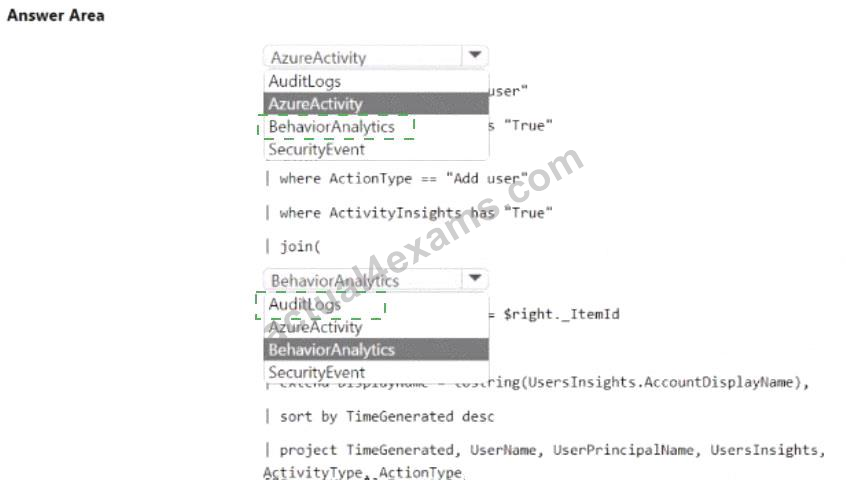
First table: BehaviorAnalytics
Joined table: AuditLogs
To detect when a user creates an unusually large number of Azure AD user accounts in Microsoft Sentinel, you should leverage UEBA signals from the BehaviorAnalytics table and enrich them with Azure AD audit data from AuditLogs. The BehaviorAnalytics table contains UEBA-derived insights (for example, the ActivityInsights flag and UsersInsights) and normalized activity fields such as ActionType (e.g., " Add user " ). Filtering BehaviorAnalytics for ActionType == " Add user " and ActivityInsights has " True " targets activities that the UEBA engine already assessed as anomalous, reducing noise and focusing on outliers.
Then, join these anomalies to the AuditLogs table to pull authoritative Azure AD audit details (target object, initiator, correlation, and operation context). This combination aligns with Sentinel guidance: use BehaviorAnalytics for anomaly detection and AuditLogs for the Azure AD operational record. Sorting by TimeGenerated and projecting user and insight fields completes the hunting query so analysts can review who triggered unusual "Add user" bursts and with what context.
Therefore, complete the query by selecting BehaviorAnalytics as the primary dataset and AuditLogs in the join (...).
Microsoft Sentinelの要件とビジネス要件を満たすには、Group1とGroup2にロールベースアクセス制御(RBAC)ロールを割り当てる必要があります。
各グループにどの役割を割り当てますか?回答するには、適切な役割を正しいグループにドラッグしてください。各役割は、1回、複数回、またはまったく使用しない場合があります。コンテンツを表示するには、ペイン間の分割バーをドラッグするか、スクロールする必要がある場合があります。
注:正解ごとに1ポイントが加算されます。
Correct Answer:

Explanation:
Group
Assign role
Group1
Logic App Contributor
Group1
Microsoft Sentinel Contributor
Group2
Microsoft Sentinel Responder
Group1 requires Microsoft Sentinel Contributor to create and manage analytics rules. It also requires Logic App Contributor to create, edit, and run Logic Apps used as Microsoft Sentinel playbooks. This combination satisfies both requirements without assigning broader permissions. Microsoft Sentinel Playbook Operator would permit manual execution but would not allow Group1 to create or modify playbooks.
Group2 requires Microsoft Sentinel Responder, which provides Microsoft Sentinel Reader permissions plus the ability to assign, update, investigate, and close incidents. Microsoft Sentinel Contributor would exceed Group2's stated responsibilities and violate least privilege. Assign the Sentinel roles at the Microsoft Sentinel resource-group level and Logic App Contributor at the resource group containing the playbooks. Microsoft Sentinel roles and permissions and playbook prerequisites.
AzureとGoogle Cloudにリソースがあります。
Google Cloud Platform (GCP) のデータを Azure Defender に取り込む必要があります。
どのような順序で操作を実行すればよいでしょうか?回答するには、操作リストからすべての操作を回答欄に移動し、正しい順序に並べ替えてください。
Correct Answer:

Explanation:
Microsoft Defender for Cloud (formerly Azure Security Center) ingests GCP security signals via a native GCP connector that reads findings from Google Cloud Security Command Center (SCC). The documented onboarding flow begins in GCP: first, enable the SCC API so the service can be invoked by tooling and service accounts. Next, configure SCC at the organization/project level (turn it on and set scope), then enable Security Health Analytics (SHA)-the built-in SCC detector that continuously evaluates resources and emits misconfiguration and vulnerability findings Defender for Cloud relies on. After telemetry is being produced, create a dedicated service account with the required reader roles and generate a private key (JSON); Defender for Cloud uses this credential to securely pull SCC findings. Finally, in Defender for Cloud, add a GCP cloud connector and provide the service account key to establish the connection and start ingestion. This sequence minimizes errors: APIs and detections are active before credentials are created, and the connector is added only after data is available, ensuring immediate validation and lowest administrative overhead.
Viewing page 1 out of 83 pages.
Viewing questions 1-5 out of 415 questions.

No help, Full refund!
Actual4Exams confidently stands behind all its offerings by giving Unconditional "No help, Full refund" Guarantee. Since the time our operations started we have never seen people report failure in the Microsoft SC-200日本語 exam after using our products. With this feedback we can assure you of the benefits that you will get from our products and the high probability of clearing the SC-200日本語 exam.
We still understand the effort, time, and money you will invest in preparing for your certification exam, which makes failure in the Microsoft SC-200日本語 exam really painful and disappointing. Although we cannot reduce your pain and disappointment but we can certainly share with you the financial loss.
This means that if due to any reason you are not able to pass the SC-200日本語 actual exam even after using our product, we will reimburse the full amount you spent on our products. you just need to mail us your score report along with your account information to address listed below within 7 days after your unqualified certificate came out.