


Achieve the 300-710 Exam Best Results with Help from Cisco Certified Experts
Provide 300-710 Practice Test Engine for Preparation
Cisco 300-710 certification exam is designed to test the knowledge and skills of IT professionals who work with Cisco Firepower. 300-710 exam covers a broad range of topics, including the installation, configuration, and management of Cisco Firepower appliances, as well as the implementation of security policies and the detection and mitigation of security threats. It also covers topics such as identity management, network access control, and advanced threat protection.
NEW QUESTION # 91
Network users experience issues when accessing a server on a different network segment. An engineer investigates the issue by performing packet capture on Cisco Secure Firewall Threat Defense. The engineer expects more data and suspects that not all the traffic was collected during a 15-minute can't captured session.
Which action must the engineer take to resolve the issue?
- A. Forward the captured data lo an FTP server
- B. Ensure that the allocated memory is sufficient.
- C. Provide a file name to save the data.
- D. Increase the amount of RAM allocated for the capture.
Answer: B
Explanation:
When performing packet capture on a Cisco Secure Firewall Threat Defense (FTD) device, ensuring that the allocated memory is sufficient is crucial for capturing all necessary traffic during a specified capture session. If users experience issues accessing a server and the engineer suspects not all traffic was collected, it indicates that the current memory allocation might not be enough to store the entire capture data for the 15-minute session.
Steps:
* Check the current memory allocation for packet captures on the FTD device.
* Increase the memory allocation if it is insufficient to handle the volume of traffic expected during the capture session.
This ensures that all relevant traffic is captured and can be analyzed to diagnose and resolve the network issue.
References: Cisco Secure Firewall Threat Defense Configuration Guide, Chapter on Packet Capture.
NEW QUESTION # 92
An administrator is adding a QoS policy to a Cisco FTD deployment. When a new rule is added to the policy and QoS is applied on 'Interfaces in Destination Interface Objects", no interface objects are available What is the problem?
- A. QoS is available only on routed interfaces, and this device is in transparent mode.
- B. The network segments that the interfaces are on do not have contiguous IP space
- C. A conflict exists between the destination interface types that is preventing QoS from being added
- D. The FTD is out of available resources lor use. so QoS cannot be added
Answer: A
NEW QUESTION # 93
An engineer must build redundancy into the network and traffic must continuously flow if a redundant switch in front of the firewall goes down. What must be configured to accomplish this task?
- A. vPC on the switches to the interface mode on the firewall duster
- B. vPC on the switches to the span EtherChannel on the firewall cluster
- C. redundant interfaces on the firewall cluster mode and switches
- D. redundant interfaces on the firewall noncluster mode and switches
Answer: B
Explanation:
Reference: https://www.ciscolive.com/c/dam/r/ciscolive/us/docs/2018/pdf/BRKSEC-2020.pdf
NEW QUESTION # 94
In a multi-tennent deployment where multiple domains are in use. which update should be applied outside of the Global Domain?
- A. local import of intrusion rules
- B. Cisco Geolocation Database
- C. minor upgrade
- D. local import of major upgrade
Answer: A
NEW QUESTION # 95
An engineer is working on a LAN switch and has noticed that its network connection to the mime Cisco IPS has gone down.
Upon troubleshooting it is determined that the switch is working as expected. What must have been implemented for this failure to occur?
- A. The Cisco IPS is configured in detection mode
- B. The upstream router has a misconfigured routing protocol
- C. The Cisco IPS has been configured to be in fail-open mode
- D. Link-state propagation is enabled
Answer: D
Explanation:
If link-state propagation is enabled on a switch, it can cause the switch to incorrectly detect a link failure, which can lead to network connectivity issues. In the case of the inline Cisco IPS, the switch may detect a link failure due to the IPS not responding to certain types of traffic, even though the IPS is functioning properly.
NEW QUESTION # 96
A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?
- A. The VLAN ID and destination MAC address are optional
- B. The destination MAC address is optional if a VLAN ID value is entered
- C. The output format option for the packet logs unavailable
- D. Only the UDP packet type is supported
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config-guide-v62/troubleshooting_the_system.html
NEW QUESTION # 97
An organization does not want to use the default Cisco Firepower block page when blocking HTTP traffic. The organization wants to include information about its policies and procedures to help educate the users whenever a block occurs. Which two steps must be taken to meet these requirements? (Choose two.)
- A. Change the HTTP response in the access control policy to custom.
- B. Create HTML code with the information for the policies and procedures.
- C. Edit the HTTP request handling in the access control policy to customized block.
- D. Write CSS code with the information for the policies and procedures.
- E. Modify the system-provided block page result using Python.
Answer: A,B
NEW QUESTION # 98
What is the result of specifying of QoS rule that has a rate limit that is greater than the maximum throughput of an interface?
- A. The system rate-limits all traffic.
- B. The system repeatedly generates warnings.
- C. Matching traffic is not rate limited.
- D. The rate-limiting rule is disabled.
Answer: C
NEW QUESTION # 99
Which limitation applies to Cisco Firepower Management Center dashboards in a multidomain environment?
- A. Child domains can view but not edit dashboards that originate from an ancestor domain.
- B. Child domains have access to only a limited set of widgets from ancestor domains.
- C. Child domains cannot view dashboards that originate from an ancestor domain.
- D. Only the administrator of the top ancestor domain can view dashboards.
Answer: C
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/firepower/60/configuration/guide/fpmc-config- guide-v60/Using_Dashboards.html
NEW QUESTION # 100
Which two remediation options are available when Cisco FMC is integrated with Cisco ISE? (Choose two.)
- A. port shutdown
- B. quarantine
- C. host shutdown
- D. dynamic null route configured
- E. DHCP pool disablement
Answer: A,B
Explanation:
Reference:
https://www.cisco.com/c/en/us/support/docs/security/identity-services-engine/210524-configure- firepower-6-1-pxgrid-remediati.html
NEW QUESTION # 101
A network administrator wants to configure a Cisco Secure Firewall Threat Defense instance managed by Cisco Secure Firewall Management Center to block traffic to known cryptomining networks. Which system settings must the administrator configure in Secure Firewall Management Center to meet the requirement?
- A. Intrusion Policy, Security Intelligence
- B. Access Policy, Rules
- C. Malware Policy, Rules
- D. Access Policy, Security Intelligence
Answer: D
Explanation:
To block traffic to known cryptomining networks using Cisco Secure Firewall Threat Defense (FTD) managed by Cisco Secure Firewall Management Center (FMC), the network administrator needs to configure Security Intelligence in an Access Control Policy. Security Intelligence allows administrators to block traffic based on threat intelligence feeds, which include known malicious IP addresses, domains, and URLs.
Steps:
Navigate to Policies > Access Control > Access Control Policy in FMC.
Edit or create an Access Control Policy.
Go to the Security Intelligence tab.
Enable the relevant threat intelligence feeds that include cryptomining networks.
Apply the policy to the FTD device.
This configuration ensures that traffic to known cryptomining networks is blocked, enhancing the network's security posture against cryptomining threats.
NEW QUESTION # 102
A network engineer sets up a secondary Cisco MC that is integrated with Cisco Security Packet Analyzer What occurs when the secondary Cisco MC synchronizes with the primary Cisco FMC?
- A. The existing configuration for integration of the secondary Cisco FMC the Cisco Security Packet Analyzer is overwritten.
- B. The existing integration configuration is replicated to the primary Cisco FMC
- C. The secondary Cisco FMC must be reintegrated with the Cisco Security Packet Analyzer after the synchronization
- D. The synchronization between the primary and secondary Cisco FMC fails
Answer: A
NEW QUESTION # 103
An engineer must configure a correlation policy in Cisco Secure Firewall Management Center to detect when an IP address from an internal network communicates with a known malicious host. Connections made by the internal IP addresses must be tracked, and an external dynamic list must be used for the condition. Which type of event must the engineer configure on the correlation policy?
- A. Malware
- B. Network discovery
- C. Connection tracker
- D. Intrusion Impact Alert
Answer: C
NEW QUESTION # 104
Refer to the exhibit.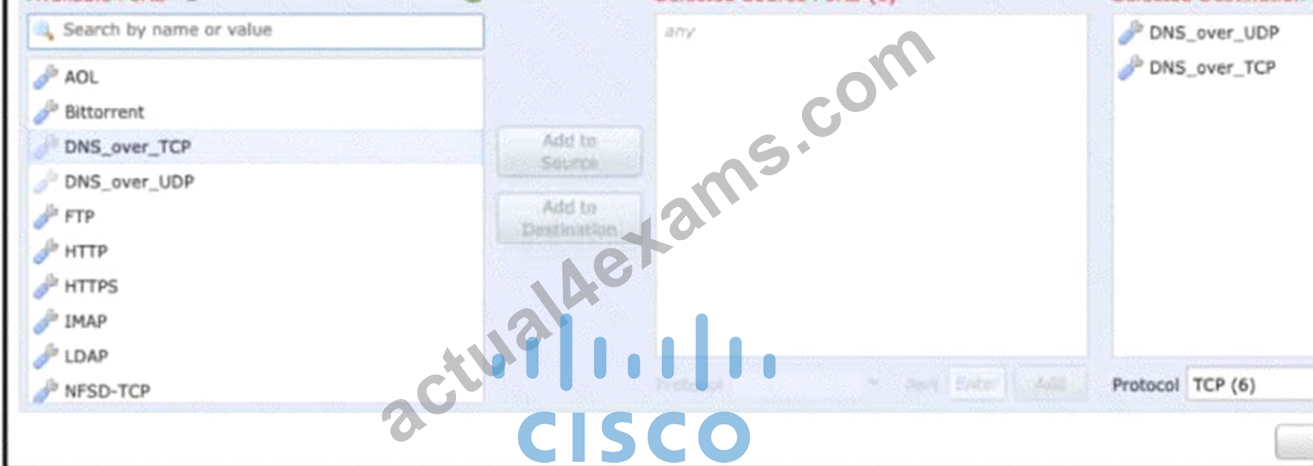
An engineer is modifying an access control policy to add a rule to Inspect all DNS traffic that passes it making the change and deploying the policy, they see that DNS traffic Is not being Inspected by the Snort engine.
What is......
- A. The rule must define the source network for inspection as well as the port.
- B. The rule Is configured with the wrong setting for the source port.
- C. The action of the rule is set to trust instead of allow.
- D. The rule must specify the security zone that originates the traffic.
Answer: C
NEW QUESTION # 105
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.
Answer:
Explanation: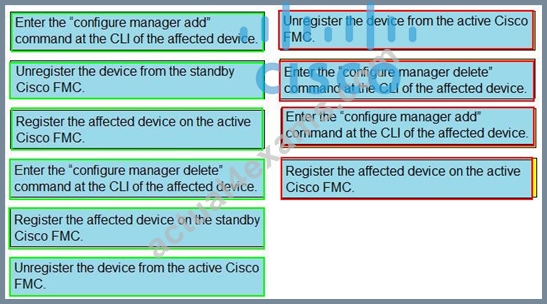
NEW QUESTION # 106
......
Cisco 300-710 certification exam is intended for network security engineers, network designers, network administrators, and security analysts who are responsible for securing enterprise networks. 300-710 exam tests the candidates on various topics related to Cisco Firepower NGFW, including advanced threat protection, policy management, network analysis and visibility, and platform architecture.
Detailed New 300-710 Exam Questions for Concept Clearance: https://latestdumps.actual4exams.com/300-710-real-braindumps.html