


Enhance Your Career With Available Preparation Guide for MD-102 Exam
Get Special Discount Offer of MD-102 Certification Exam Sample Questions and Answers
Microsoft MD-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 32
What should you upgrade before you can configure the environment to support co-management?
- A. Configuration Manager
- B. the domain functional level
- C. the domain controllers
- D. Windows Server Update Services (WSUS)
Answer: A
Explanation:
References:
https://docs.microsoft.com/en-us/sccm/comanage/tutorial-co-manage-clients
Topic 3, Contoso Ltd, Case 2
Overview
Contoso, Ltd, is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
Contoso has the users and computers shown in the following table.
The company has IT, human resources (HR), legal (LEG), marketing (MKG) and finance (FIN) departments.
Contoso uses Microsoft Store for Business and recently purchased a Microsoft 365 subscription.
The company is opening a new branch office in Phoenix. Most of the users in the Phoenix office will work from home.
Existing Environment
The network contains an Active Directory domain named contoso.com that is synced to Microsoft Azure Active Directory (Azure AD).
All member servers run Windows Server 2016. All laptops and desktop computers run Windows 10 Enterprise.
The computers are managed by using Microsoft System Center Configuration Manager. The mobile devices are managed by using Microsoft Intune.
The naming convention for the computers is the department acronym, followed by a hyphen, and then four numbers, for example, FIN-6785. All the computers are joined to the on-premises Active Directory domain.
Each department has an organization unit (OU) that contains a child OU named Computers. Each computer account is in the Computers OU of its respective department.
Intune Configuration
Requirements
Planned Changes
Contoso plans to implement the following changes:
* Provide new computers to the Phoenix office users. The new computers have Windows 10 Pro preinstalled and were purchased already.
* Start using a free Microsoft Store for Business app named App1.
* Implement co-management for the computers.
Technical Requirements:
Contoso must meet the following technical requirements:
* Ensure that the users in a group named Group4 can only access Microsoft Exchange Online from devices that are enrolled in Intune.
* Deploy Windows 10 Enterprise to the computers of the Phoenix office users by using Windows Autopilot.
* Monitor the computers in the LEG department by using Windows Analytics.
* Create a provisioning package for new computers in the HR department.
* Block iOS devices from sending diagnostic and usage telemetry data.
* Use the principle of least privilege whenever possible.
* Enable the users in the MKG department to use App1.
* Pilot co-management for the IT department.
NEW QUESTION # 33
You have an Azure Active Directory (Azure AD) tenant named adatum.com that contains two computers named Computer1 and Computer2. The computers run Windows 10 and are members of a group named GroupA.
The tenant contains a user named User1 that is a member of a group named Group1.
You need to ensure that if User1 changes the desktop background on Computer1, the new desktop background will appear when User1 signs in to Computer2.
What should you do?
- A. From the Azure Active Directory admin center, enable Enterprise State Roaming for GroupA.
- B. Create a device configuration profile for Windows 10 and configure the Shared multi-user device settings. Assign the profile to GroupA.
- C. From the Azure Active Directory admin center, enable Enterprise State Roaming for Group1.
- D. Create a device configuration profile for Windows 10 and configure the Shared multi-user device settings. Assign the profile to Group1.
Answer: C
Explanation:
Enterprise State Roaming provides users with a unified experience across their Windows devices and reduces the time needed for configuring a new device.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/devices/enterprise-state-roaming-enable
NEW QUESTION # 34
You have a Microsoft 365 subscription.
All users have Microsoft 365 apps deployed.
You need to configure Microsoft 365 apps to meet the following requirements:
* Enable the automatic installation of WebView2 Runtime.
* Prevent users from submitting feedback.
Which two settings should you configure in the Microsoft 365 Apps admin center? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
You can enable automatic installation in the same setting as where you prevent it from being installed automatically:
To prevent the automatic installation of WebView2 Runtime, sign in to the Microsoft 365 Apps admin center (https://config.office.com) with an admin account. Then, go to Customization > Device Configuration > Modern Apps Settings. Select Microsoft Edge WebView2 and then clear the Enable automatic installation of WebView2 Runtime check box.
https://learn.microsoft.com/en-us/deployoffice/webview2-install
Prevent users from submitting feedback:
https://learn.microsoft.com/en-us/microsoft-365/admin/manage/manage-feedback-ms-org?view=o365-worldwid
NEW QUESTION # 35
Your company purchases new computers that run Windows 10. The computers have cameras that support Windows Hello for Business.
You configure the Windows Hello for Business Group Policy settings as shown in the following exhibit.
What are two valid methods a user can use to sign in? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. A PIN
- B. Facial recognition
- C. A smartwatch that is Bluetooth-enabled
- D. A USB key
Answer: A,B
Explanation:
Facial recognition and pin are the only choices to be able to sign in. A smartwatch that is Bluetooth-enabled has to do with locking the Windows device.
NEW QUESTION # 36
Your network contains an Active Directory domain named contoso.com. The domain contains a computer named Computer1 that runs Windows 10. You have the groups shown in the following table.
Which groups can you add to Group4?
- A. Group1, Group2, and Group3
- B. Group2 and Group3 only
- C. Group2only
- D. Group1 and Group2 only
Answer: B
NEW QUESTION # 37
You have a Microsoft 365 ES subscription that uses Microsoft Intune.
Devices are enrolled in Intune as shown in the following table.
The devices are the members of groups as shown in the following table.
You create an JOS/iPadOS update profile as shown in the following exhibit.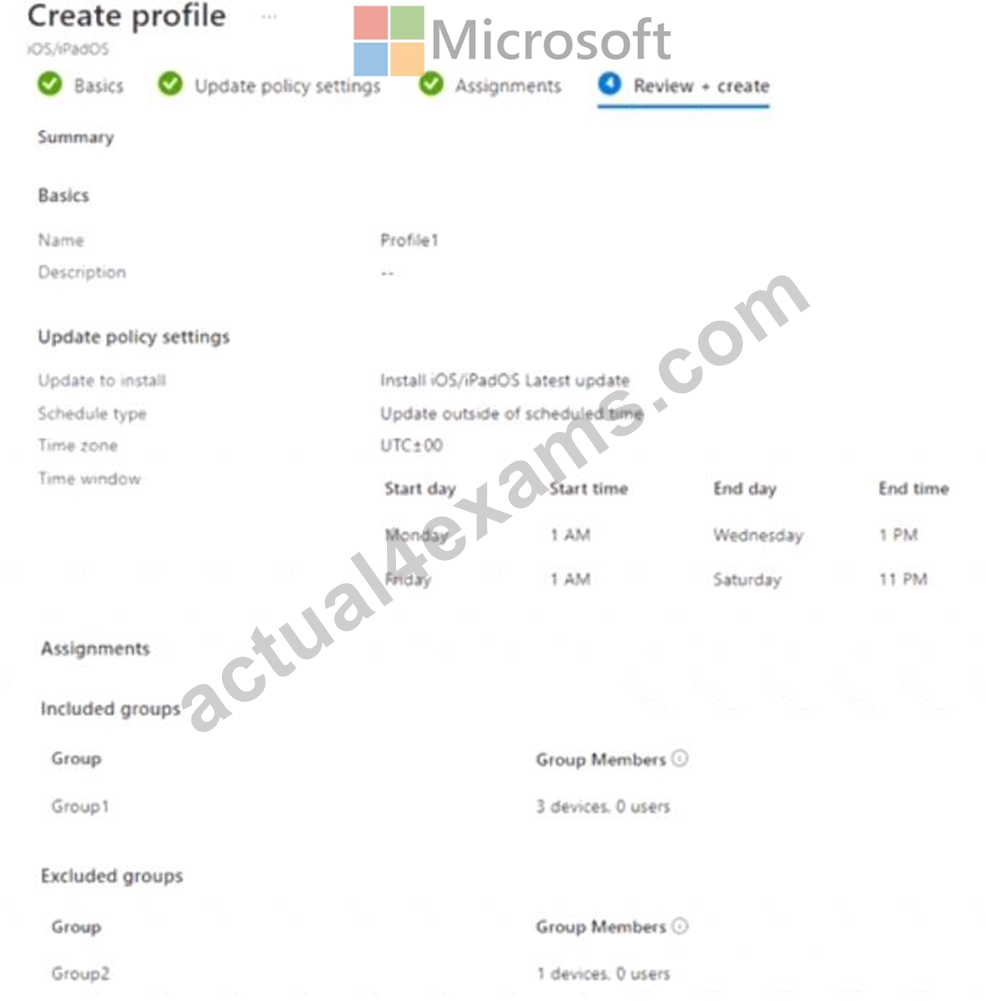
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 38
You have 100 computers that run Windows 10. You have no servers. All the computers are joined to Microsoft Azure Active Directory (Azure AD).
The computers have different update settings, and some computers are configured for manual updates.
You need to configure Windows Update. The solution must meet the following requirements:
The configuration must be managed from a central location.
Internet traffic must be minimized.
Costs must be minimized.
How should you configure Windows Update? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows-server/administration/windows-server-update-services/deploy/4-configure-group-policy-settings-for-automatic-updates
NEW QUESTION # 39
You have a Microsoft Deployment Toolkit (MDT) solution that is used to manage Windows 11 deployment tasks.
MDT contains the operating system images shown in the following table.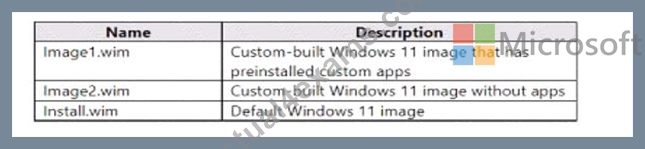
You need to perform a Windows 11 in-place upgrade on several computers that run Windows 10.
From the Deployment Workbench, you open the New Task Sequence Wizard.
You need to identify which task sequence template and which operating system image to use for the task sequence. The solution must minimize administrative effort.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Standard Client Upgrade Task Sequence
Use Template: Standard Client Upgrade Task Sequence
In-place upgrade is the preferred method to use when migrating from Windows 10 to a later release of Windows 10, and is also a preferred method for upgrading from Windows 7 or 8.1 if you do not plan to significantly change the device's configuration or applications. MDT includes an in-place upgrade task sequence template that makes the process really simple.
Box 2: Install.wim
In-place upgrade differs from computer refresh in that you cannot use a custom image to perform the in-place upgrade. I Reference:
https://docs.microsoft.com/en-us/windows/deployment/deploy-windows-mdt/upgrade-to-windows-10-with-the-m
NEW QUESTION # 40
You need to recommend a solution to meet the device management requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Reference:
https://github.com/MicrosoftDocs/IntuneDocs/blob/master/intune/app-protection-policy.md
https://docs.microsoft.com/en-us/azure/information-protection/configure-usage-rights#do-not-forward-option-for
NEW QUESTION # 41
User1 and User2 plan to use Sync your settings.
On which devices can the users use Sync your settings? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: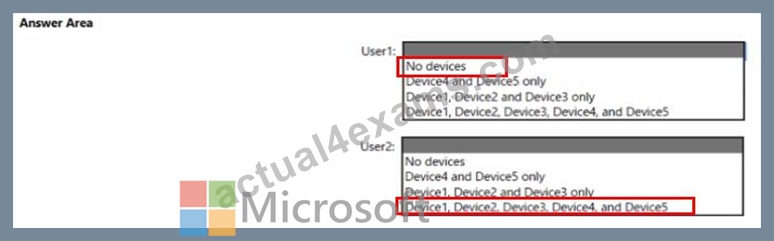
Reference:
https://www.jeffgilb.com/managing-local-administrators-with-azure-ad-and-intune/
NEW QUESTION # 42
You have a Microsoft 365 E5 subscription that contains 100 Windows 10 devices enrolled in Microsoft Intune.
You need to create Endpoint security policies to meet the following requirements:
* Hide the Firewall & network protection area in the Windows Security app.
* Disable the provisioning of Windows Hello for Business on the devices.
Which two policy types should you use? To answer, select the policies in the answer area.
NOTE: Each correct selection is worth one point.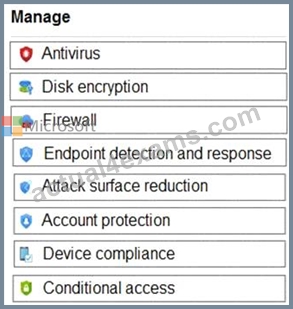
Answer:
Explanation:
Explanation:
In the Antivirus policy settings, you can hide the Firewall and network protection area in the Windows Security app.
Windows Hello for Business settings are configured in Identity protection.
Reference:
https://docs.microsoft.com/en-us/mem/intune/protect/antivirus-security-experience-windows-settings
https://docs.microsoft.com/en-us/mem/intune/protect/identity-protection-windows-settings
NEW QUESTION # 43
You have a Windows 11 capable device named Device1 that runs the 64-bit version of Windows
10 Enterprise and has Microsoft Office 2019 installed.
You have the Windows 11 Enterprise images shown in the following table.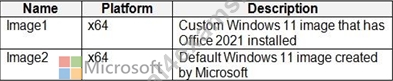
Which images can be used to perform an in-place upgrade of Device1?
- A. lmage2 only
- B. Image1 and Image2
- C. image1 only
Answer: A
Explanation:
https://learn.microsoft.com/en-us/windows/deployment/windows-10-deployment-scenarios Existing applications are preserved through the process. So, the upgrade process uses the standard Windows installation media image (Install.wim). Custom images aren't needed and can't be used because the upgrade process is unable to deal with conflicts between apps in the old and new operating system.
NEW QUESTION # 44
You have a Microsoft 365 subscription that uses Microsoft Intune.
You plan to use Windows Autopilot to provision 25 Windows 11 devices.
You need to meet the following requirements during device provisioning:
* Display the progress of app and profile deployments.
* Join the devices to Azure AD.
What should you configure to meet each requirement? To answer drag the appropriate settings to the correct requirements. Each setting may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 45
You have the device configuration profile shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 46
You have a Microsoft Intune subscription that has the following device compliance policy settings:
Mark devices with no compliance policy assigned as: Compliant
Compliance status validity period (days): 14
On January 1, you enroll Windows 10 devices in Intune as shown in the following table.
On January 4, you create the following two device compliance policies:
Name: Policy1
Platform: Windows 10 and later
Require BitLocker: Require
Mark device noncompliant: 5 days after noncompliance
Scope (Tags): Tag1
Name: Policy2
Platform: Windows 10 and later
Firewall: Require
Mark device noncompliant: Immediately
Scope (Tags): Tag2
On January 5, you assign Policy1 and Policy2 to Group1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.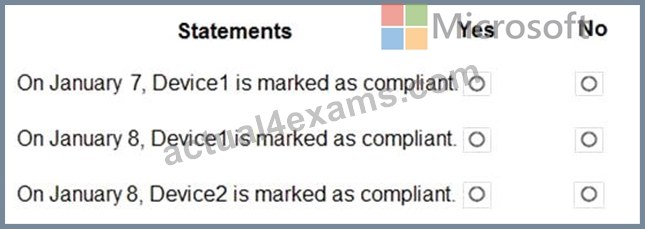
Answer:
Explanation: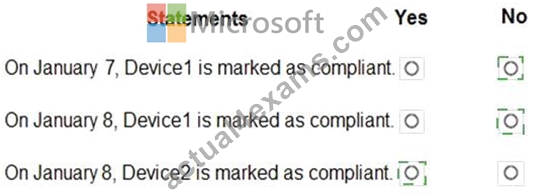
Explanation:
Box 1: No.
Policy1 and Policy2 apply to Group1 which Device1 is a member of. Device1 does not meet the firewall requirement in Policy2 so the device will immediately be marked as non-compliant.
Box 2: No
For the same reason as Box1.
Box 3: Yes
Policy1 and Policy2 apply to Group1. Device2 is not a member of Group1 so the policies don't apply.
The Scope (tags) have nothing to do with whether the policy is applied or not. The tags are used in RBAC.
NEW QUESTION # 47
You have a Microsoft Intune subscription.
You are creating a Windows Autopilot deployment profile named Profile1 as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 48
You have a Microsoft 365 tenant and an internal certification authority (CA).
You need to use Microsoft Intune to deploy the root CA certificate to managed devices.
Which type of Intune policy and profile should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 49
Drag and Drop Question
You have a Microsoft 365 E5 subscription that includes Microsoft Intune.
The subscription contains Android Enterprise devices that are enrolled in Intune and have personally-owned work profiles. All the Android devices are members of a group named Group1.
You need to ensure that end users and Intune administrators receive an email message when an Android device does NOT have an up-to-date security provider.
Which actions should you perform from the Microsoft Intune admin center in sequence? To answer, drag the appropriate actions to the correct order. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: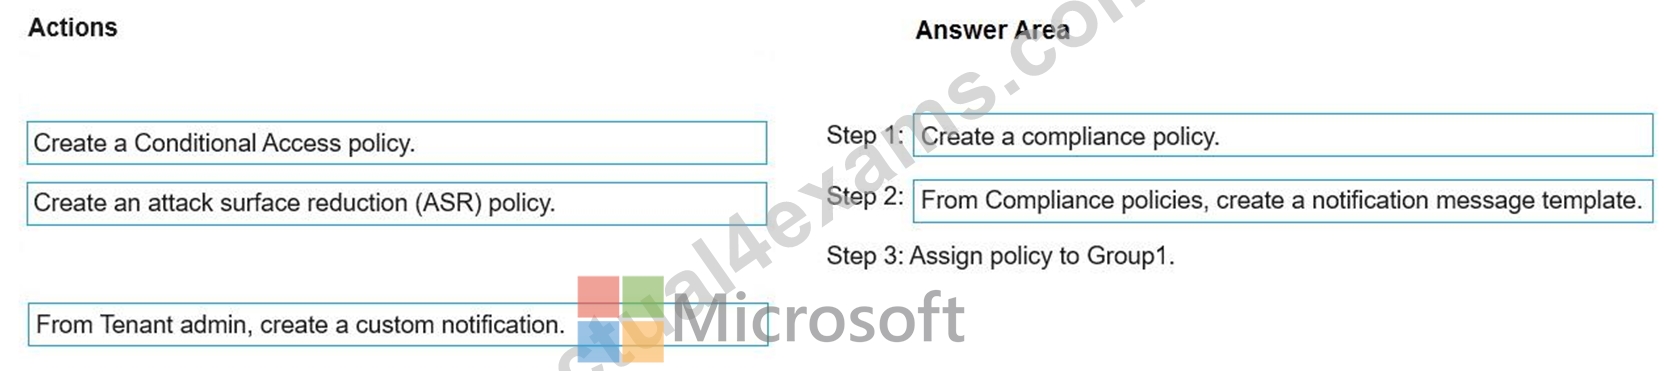
NEW QUESTION # 50
You have an Azure AD tenant named contoso.com.
You plan to use Windows Autopilot to configure the Windows 10 devices shown in the following table.
Which devices can be configured by using Windows Autopilot self-deploying mode?
- A. Device2 only
- B. Device2 and Devnce3 only
- C. Device 1, Device2, and Device3
- D. Device3 only
Answer: B
Explanation:
Windows Autopilot self-deploying mode requires devices that have a firmware-embedded activation key for Windows 10 Pro or Windows 11 Pro. This feature allows devices to automatically activate Windows Enterprise edition using the subscription license assigned to the user. Device1 does not have a firmware-embedded activation key, so it cannot use self-deploying mode. Device2 and Device3 have firmware-embedded activation keys for Windows 10 Pro, so they can use self-deploying mode. Reference: Windows Autopilot self-deploying mode (Public Preview), Deploy Windows Enterprise licenses
NEW QUESTION # 51
Hotspot Question
You have the on-premises servers shown in the following table.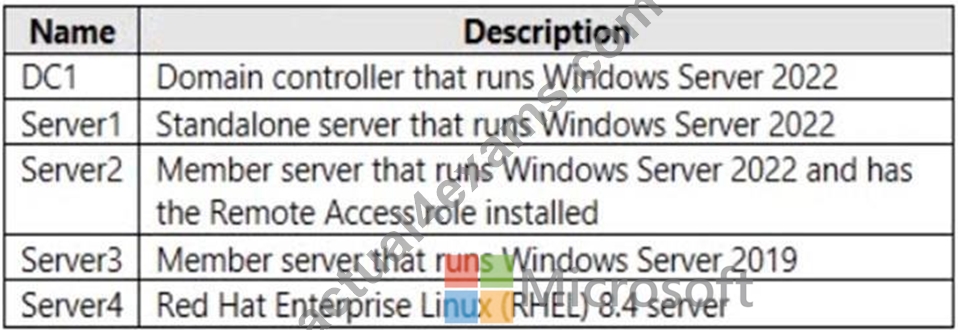
You have a Microsoft 365 E5 subscription that contains Android and iOS devices. All the devices are managed by using Microsoft Intune.
You need to implement Microsoft Tunnel for Intune. The solution must minimize the number of open firewall ports.
To which server can you deploy a Tunnel Gateway server, and which inbound ports should be allowed on the server to support Microsoft Tunnel connections? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: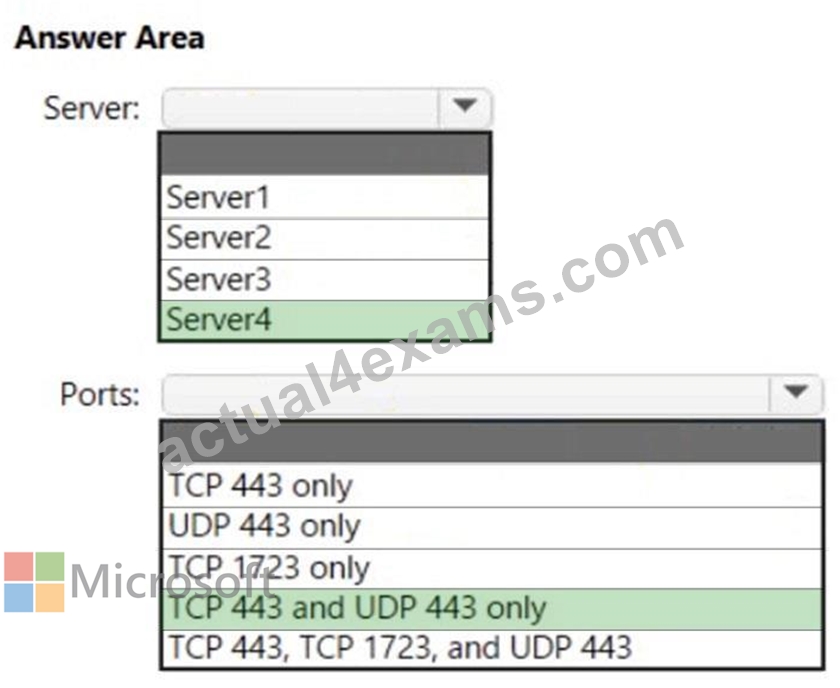
Explanation:
Box 1: Server4
Microsoft Tunnel is a VPN gateway solution for Microsoft Intune that runs in a container on Linux and allows access to on-premises resources from iOS/iPadOS and Android Enterprise devices using modern authentication and Conditional Access.
Box 2: TCP 443 and UDP 443 only
Some traffic goes to your public facing IP address for the Tunnel. The VPN channel will use TCP, TLS, UDP, and DTLS over port 443.
By default, port 443 is used for both TCP and UDP, but this can be customized via the Intune Server Configuration" Server port setting. If changing the default port (443) ensure your inbound firewall rules are adjusted to the custom port.
Reference:
https://docs.microsoft.com/en-us/mem/intune/protect/microsoft-tunnel-overview
NEW QUESTION # 52
......
Updated MD-102 Dumps Questions Are Available For Passing Microsoft Exam: https://latestdumps.actual4exams.com/MD-102-real-braindumps.html